
-
×InformationNeed Windows 11 help?Check documents on compatibility, FAQs, upgrade information and available fixes.
Windows 11 Support Center. -
-
×InformationNeed Windows 11 help?Check documents on compatibility, FAQs, upgrade information and available fixes.
Windows 11 Support Center. -
- HP Community
- Gaming
- Gaming Desktops
- Secure Boot Key Firmware
Create an account on the HP Community to personalize your profile and ask a question
Your account also allows you to connect with HP support faster, access a personal dashboard to manage all of your devices in one place, view warranty information, case status and more.
10-04-2026 10:52 PM
 HP Recommended
Product: OMEN 30L Desktop - GT13-0024
HP OMEN 30L GT13-0024, motherboard 87C3, BIOS F.32. The motherboard was replaced in August 2026. Windows 11's Secure Boot servicing infrastructure is present and the Secure-Boot-Update scheduled task runs, but Windows UEFI CA 2023 never gets added to the firmware DB. WindowsUEFICA2023Capable remains 0 and UEFICA2023Status returns to NotStarted after reboot. The active db and dbDefault both lack Windows UEFI CA 2023. PK, KEK, and DB are present with authenticated-write attributes (39). There is no newer BIOS available. The previous motherboard had Secure Boot Event 1808 entries in July 2026; the replacement motherboard has had none since installation.
Please verify whether this replacement board's firmware/Secure Boot variable provisioning supports the Windows UEFI CA 2023 certificate update, and whether there is an HP-specific procedure or firmware-side fix for this replacement motherboard.
5 REPLIES 5


10-06-2026 02:05 PM
HP Recommended
Hi @P3rsonas
Welcome to the HP Support Community.
Thank you for posting your query.
I understand your concern regarding the Windows UEFI CA 2023 certificate not being provisioned after the motherboard replacement. Since the replacement motherboard is already running BIOS F.32 and the certificate is not appearing in the Secure Boot DB, I would like to verify the current Secure Boot key configuration and provisioning status before determining whether this is a firmware limitation. Could you please confirm from where the replacement was done. Also,
- Could you please confirm whether the replacement motherboard is still using the factory-provisioned Secure Boot keys and certificates?
- Have you checked whether Windows UEFI CA 2023 is present in the firmware’s dbDefault variable, or is it completely absent?
- Have you tried restoring the BIOS Secure Boot keys to factory defaults and then rebooting to check whether the Windows UEFI CA 2023 certificate is provisioned?
- Does Secure Boot currently show as enabled and active in the BIOS and Windows System Information (msinfo32)?
- Have there been any BIOS/Secure Boot key changes, or manual key enrollment performed after the motherboard replacement?
- Can you confirm whether the previous motherboard and replacement motherboard have the same motherboard/system board ID (87C3)?
Take care and have an amazing day!
I'm an HP Employee.
If this reply helped resolve your issue, please select the Accept as Solution as it helps others in the community quickly find the answer they’re looking for.
And if you found this reply helpful, clicking Yes below is a great way to let us know we’re providing the support you need, as it encourages us to keep improving and sharing helpful guidance.
10-06-2026 08:06 PM
HP Recommended
Thank you for the detailed response. I can confirm the following:
The replacement motherboard was installed by HP/service personnel in August 2026. I no longer have the previous motherboard.
The replacement motherboard appears to still be using its factory-provisioned Secure Boot keys. I have not manually enrolled or replaced any Secure Boot keys.
I checked the firmware dbDefault variable. Windows UEFI CA 2023 is completely absent from dbDefault, as well as from the currently active db.
I have not restored or cleared the Secure Boot keys to factory defaults. The BIOS currently shows “Load HP Factory Default Keys” as grayed out, while “Clear All Secure Boot Keys” is available. I have intentionally not used “Clear All Secure Boot Keys” because I do not want to remove the currently enrolled keys without confirming that this is safe and supported for this motherboard.
Secure Boot is currently disabled in both the BIOS and Windows (msinfo32 shows Secure Boot State: Off). The BIOS does show Platform Key as Enrolled, and PK, KEK, and DB are all present.
I have not manually enrolled any Secure Boot keys or certificates after the motherboard replacement. I have only performed the Windows Secure Boot certificate update procedure, including running the Secure-Boot-Update scheduled task.
Both the previous and replacement motherboards are the same board model: HP 87C3. The replacement motherboard was installed in August 2026.
In the BIOS, “Load HP Factory Default Keys” is grayed out/unavailable, while “Clear All Secure Boot Keys” is available. I have not selected “Clear All Secure Boot Keys” because I do not want to remove the currently enrolled Secure Boot keys without confirmation that this is the correct procedure for this replacement motherboard.
For additional context, the replacement board is running AMI BIOS F.32, and there is currently no newer BIOS available for the OMEN 30L GT13-0024.
The important difference I have found is that the previous motherboard had Windows Secure Boot Event 1808 entries in July 2026, including updates for Windows UEFI CA 2023, while the replacement motherboard has had no corresponding Secure Boot certificate update events since it was installed.
The current firmware db contains the existing HP and Microsoft Secure Boot certificates, but not Windows UEFI CA 2023. Windows reports WindowsUEFICA2023Capable = 0, and after attempting the Microsoft Secure Boot update procedure, UEFICA2023Status returns to NotStarted after reboot.
Could you please confirm whether restoring the factory Secure Boot keys is actually required/supported on this specific 87C3 replacement motherboard before I do so? I do not want to clear or modify the existing Secure Boot key database unless HP confirms that it is the appropriate procedure.
If possible, I would also appreciate verification of whether this replacement board's firmware/Secure Boot provisioning supports the Windows UEFI CA 2023 update.
10-07-2026 03:10 PM
HP Recommended
Hi @P3rsonas
Thank you for providing the detailed information and for clarifying the Secure Boot configuration of the replacement motherboard.
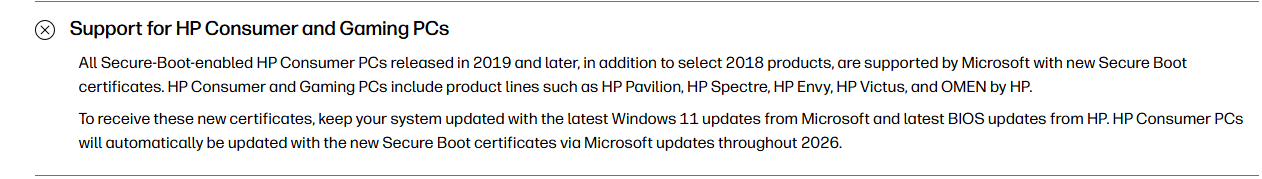
The information you shared is helpful. However, based on the HP guidance shown in the provided documentation, Secure Boot-enabled HP Consumer and Gaming PCs released in 2019 and later are supported for the new Secure Boot certificates, and the Windows UEFI CA 2023 certificates are expected to be delivered automatically through Microsoft Windows updates during 2026, provided the system is kept updated with the latest BIOS and Windows 11 updates.
Click here for more information.
Have a good day.
I'm an HP Employee.
If this reply helped resolve your issue, please select the Accept as Solution as it helps others in the community quickly find the answer they’re looking for.
And if you found this reply helpful, clicking Yes below is a great way to let us know we’re providing the support you need, as it encourages us to keep improving and sharing helpful guidance.
10-07-2026 04:51 PM
HP Recommended
Thank you for the information. I understand that HP Consumer and Gaming PCs released in 2019 and later are supported for the new Secure Boot certificates, and that the certificates are expected to be delivered through Windows updates.
However, that is what makes the current behavior of my replacement motherboard confusing. My concern is not whether the OMEN 30L GT13-0024 is generally supported, but why the certificate update is not actually being provisioned on this specific replacement motherboard.
I have already allowed Windows to perform the Secure Boot certificate update, including running the Microsoft-documented Secure-Boot-Update scheduled task. The task runs, but Windows UEFI CA 2023 is never added to the firmware DB.
The Secure Boot certificate rollout has also technically already reached this PC. The previous motherboard generated multiple Secure Boot Event 1808 entries in July 2026, including Windows UEFI CA 2023 updates. However, that motherboard was replaced in August 2026, so those events occurred before the current motherboard was installed. Since the replacement, the certificate update has not completed on the new motherboard.
Specifically:
WindowsUEFICA2023Capable remains 0.
UEFICA2023Status returns to NotStarted after reboot rather than becoming Updated.
Windows UEFI CA 2023 is completely absent from both the active firmware db and dbDefault.
The replacement motherboard is HP 87C3 and is running BIOS F.32, with no newer BIOS currently available.
PK, KEK, and DB are present.
I have not manually changed or enrolled Secure Boot keys.
In the BIOS, “Load HP Factory Default Keys” is grayed out/unavailable, while “Clear All Secure Boot Keys” is available. I have not used the Clear option because I do not want to remove the existing Secure Boot keys without confirmation that this is the correct procedure.
The previous 87C3 motherboard had multiple Secure Boot Event 1808 entries in July 2026, including Windows UEFI CA 2023 updates. The replacement motherboard was installed in August 2026 and has not generated corresponding Secure Boot certificate update events since installation.
Therefore, could you please clarify whether the replacement motherboard's firmware is correctly provisioned for the Windows UEFI CA 2023 update?
In particular, I would like to know:
Why is Windows UEFI CA 2023 absent from dbDefault on the replacement motherboard if this system is supported?
Why is “Load HP Factory Default Keys” grayed out in the BIOS?
Is there an HP-specific firmware procedure, BIOS configuration, or service action required to provision the 2023 Secure Boot certificates on a replacement 87C3 motherboard?
Should I perform “Clear All Secure Boot Keys” despite “Load HP Factory Default Keys” being unavailable? I would prefer not to do this unless HP specifically confirms that it is safe and supported for this motherboard.
I understand that the general HP guidance states that these certificates should be delivered automatically. My question is specifically why that automatic process is failing on this replacement motherboard despite the system being supported, and whether the fact that the original motherboard already received the rollout has any effect on the replacement motherboard's ability to receive it.
10-09-2026 05:55 AM
HP Recommended
Hi @P3rsonas
Thank you for responding.
I understand that your concern is specifically related to the Secure Boot certificate provisioning on the replacement HP 87C3 motherboard running BIOS F.32, rather than the general compatibility of the OMEN 30L GT13-0024 with the Windows UEFI CA 2023 certificate update.
Since WindowsUEFICA2023Capable remains 0, UEFICA2023Status returns to NotStarted, and the Windows UEFI CA 2023 certificate is absent from both db and dbDefault, the issue requires further investigation into the replacement motherboard's firmware configuration and certificate provisioning.
Since WindowsUEFICA2023Capable remains 0, UEFICA2023Status returns to NotStarted, and the Windows UEFI CA 2023 certificate is absent from both db and dbDefault, the issue requires further investigation into the replacement motherboard's firmware configuration and certificate provisioning.
I recommend reaching out to the Service Center to verify the replacement motherboard's Secure Boot firmware provisioning, the availability of a compatible BIOS update or service procedure, and the reason the Windows UEFI CA 2023 update is not completing.
I will take this as feedback regarding the certificate update behavior on replacement motherboards and the need for clearer, model-specific guidance when the standard Windows update process does not work as expected.
Have a good day.
I'm an HP Employee.
If this reply helped resolve your issue, please select the Accept as Solution as it helps others in the community quickly find the answer they’re looking for.
And if you found this reply helpful, clicking Yes below is a great way to let us know we’re providing the support you need, as it encourages us to keep improving and sharing helpful guidance.

Be alert for scammers posting fake support phone numbers and/or email addresses on the community.
If you think you have received a fake HP Support message, please report it to us by clicking on "Flag Post".
† The opinions expressed above are the personal opinions of the authors, not of HP. By using this site, you accept the Terms of Use and Rules of Participation.


Didn't find what you were looking for?
Ask the community
† The opinions expressed above are the personal opinions of the authors, not of HP. By using this site, you accept the <a href="https://www8.hp.com/us/en/terms-of-use.html" class="udrlinesmall">Terms of Use</a> and <a href="/t5/custom/page/page-id/hp.rulespage" class="udrlinesmall"> Rules of Participation</a>.